Object Storage Security: A Practical Checklist
Object storage security keeps backups, media, and business data protected. Learn practical access, encryption, monitoring, and recovery controls for teams.
ACMMAX Insights ·
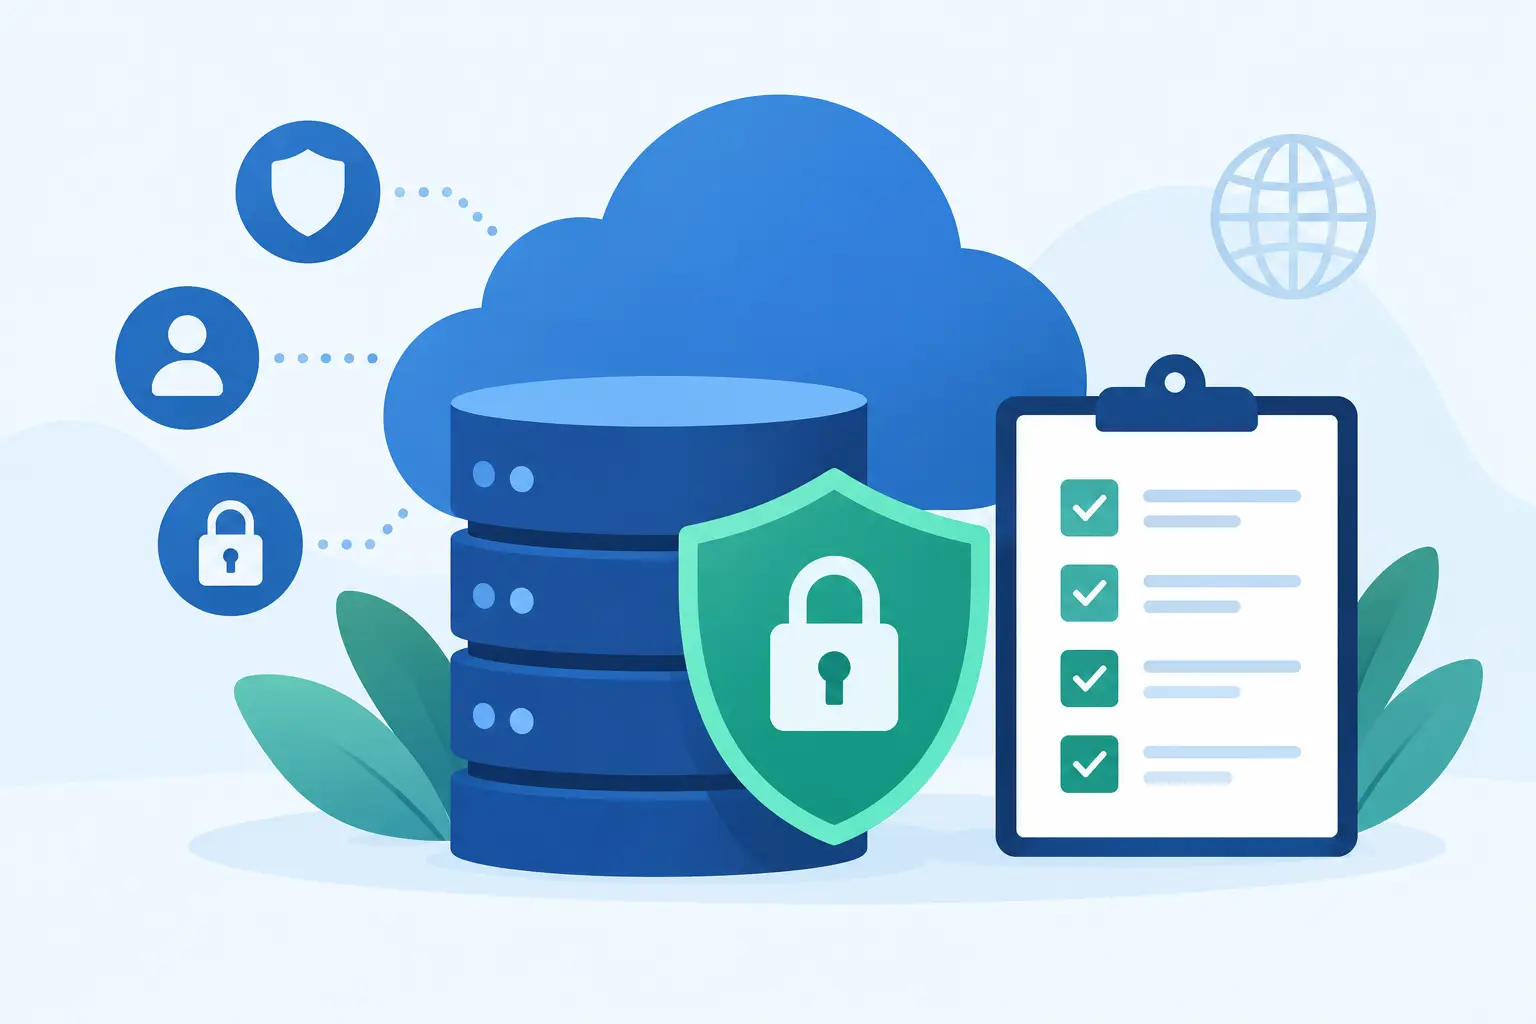
A private customer backup can become public in seconds when one bucket policy is wrong. That is why object storage security is not a feature you turn on once and forget. It is a set of operating decisions: who can access data, what they can do with it, how long it is retained, and how quickly you can prove what happened if something goes wrong.
For entrepreneurs, agencies, developers, and growing businesses, object storage often becomes the home for the assets that keep operations moving. Website media, database backups, invoices, application logs, product files, client exports, and archive data can all live in one place. That centralization is efficient, but it also raises the cost of a misconfigured permission or exposed access key.
Why object storage security deserves attention
Object storage is built for scale. Instead of managing traditional folders and disk volumes, you store files as objects in buckets and access them through a dashboard, API, or S3-compatible tools. That flexibility is useful for websites, apps, backups, and automated workflows, but it also means permissions can be managed in several places at once.
A bucket may look private in the storage dashboard while an application access key has broader permissions than intended. A temporary public link may remain active too long. A backup policy may preserve data but fail to protect it from deletion or ransomware. Security depends on the full setup, not a single setting.
The goal is not to make storage difficult to use. The goal is to give every user, application, and process only the access it needs, then make that access visible and recoverable.
Start with access control, not convenience
Most object storage incidents begin with access that is too broad. A shared administrator account, a hard-coded key in a website repository, or a bucket configured for public reads can expose far more data than a business intended.
Apply least-privilege access from the beginning. A website that only needs to display product images should be able to read from the specific media bucket it uses. It should not be able to delete backups, create new users, or access every bucket in the account. A backup tool should be allowed to write to a backup location, while restoration rights can be limited to a smaller group.
Separate people from applications. Team members should use individual accounts so actions can be traced to a specific person. Applications should use dedicated service credentials with narrowly scoped permissions. Avoid one shared key for every site, script, and contractor. When a project ends or a credential is exposed, you want to revoke one access path without breaking the rest of your operation.
Public access has a legitimate place, especially for website images, downloads, and static files. Treat it as an explicit publishing choice, not the default. Keep customer records, backups, private documents, log files, and configuration exports in private buckets. If a file needs limited external access, a time-limited signed URL is usually safer than making the full bucket public.
Protect access keys like passwords
Access keys can provide direct programmatic access to storage, often without requiring a user to sign in to a dashboard. Store them in environment variables or a dedicated secrets manager, not in source code, browser-side JavaScript, screenshots, or unencrypted documents.
Rotate credentials on a schedule and immediately after a team departure, suspected exposure, or application compromise. Rotation takes planning because a poorly coordinated key change can interrupt backups or media uploads. The practical approach is to create a replacement key, update the application, test it, then disable the old key. This reduces downtime while removing unnecessary risk.
Encrypt data in transit and at rest
Encryption protects data from being read if it is intercepted or accessed outside approved controls. For data in transit, require HTTPS and secure API connections. This is especially relevant when remote employees, client systems, websites, or automation tools connect to storage over the internet.
For data at rest, use server-side encryption for buckets that contain business or customer information. Depending on your platform and compliance requirements, you may use provider-managed encryption keys or customer-managed keys. Provider-managed keys are simpler and reduce operational overhead. Customer-managed keys can offer more control over key rotation, access, and audit requirements, but they also introduce responsibility. Losing access to a customer-managed key can make stored data unavailable.
Do not assume encryption replaces permissions. Encrypted objects can still be exposed when an authorized account is compromised or a bucket policy allows public access. Encryption and access control work together.
Build recovery into the storage design
A deleted object is not always a recoverable object. A ransomware event, an accidental cleanup script, or a mistaken overwrite can remove critical data faster than a small team can react. Recovery controls need to be configured before an incident, not during one.
Versioning is one of the most useful protections for important buckets. When enabled, it retains previous versions of an object after changes or deletion. If a file is overwritten with a bad export or removed by mistake, you may be able to restore an earlier version. The trade-off is storage consumption. Old versions can accumulate quickly in high-change workloads, so pair versioning with lifecycle rules that fit your recovery window.
For highly sensitive backups and records, consider object locking or immutability controls where available. These settings can prevent deletion or modification for a defined retention period. They are valuable for ransomware resilience and regulated recordkeeping, but use them carefully. An overly long retention policy can create unnecessary costs and make normal data cleanup harder.
A practical recovery plan should answer three questions: Which buckets are business-critical? How far back do you need to recover? Who has authority to restore data? Test the answers with a real restore. A backup that has never been restored is only an assumption.
Monitor activity before it becomes an incident
Logging is what turns a storage event into an understandable event. Enable audit logs where available and retain records of authentication attempts, bucket policy changes, object deletions, and permission updates. If a customer asks why a file disappeared, or an employee reports unusual activity, these records help establish what happened.
Set alerts for high-impact events rather than trying to alert on everything. Useful triggers include public-access changes, repeated failed authentication attempts, creation of new administrator credentials, bulk object deletions, and unusually large data transfers. The right threshold depends on your workload. A media-heavy website may transfer large volumes normally, while a small accounting archive should not suddenly send gigabytes of data to an unfamiliar location.
Review access periodically. Businesses change quickly: contractors finish projects, applications are replaced, and old environments remain online longer than expected. A quarterly review of users, keys, bucket policies, and public buckets catches many problems before they become incidents.
Use lifecycle policies to reduce risk and cost
Keeping every file forever is not a security strategy. Old temporary exports, duplicate uploads, failed job artifacts, and obsolete backups expand the amount of data that could be exposed. They also raise storage costs and make recovery harder to manage.
Lifecycle policies automate retention. You can expire temporary files after a short period, transition old archives to lower-cost storage where supported, or remove old object versions after your defined recovery window. The key is classification. A disposable image-processing file may need seven days. Financial records, legal documents, and production backups may need much longer retention.
Document these rules in plain language so your team understands what will be deleted and when. Automation is valuable, but only when its consequences are clear.
A practical object storage security baseline
For most small and mid-sized businesses, a strong starting point includes these controls:
- Keep buckets private by default and make individual assets public only when required.
- Use separate, least-privilege credentials for users, websites, backup tools, and automation.
- Require encrypted connections and enable encryption at rest for sensitive data.
- Turn on versioning for critical buckets, then define retention and lifecycle rules.
- Protect access keys, rotate them regularly, and remove unused credentials immediately.
- Enable activity logs and alerts for policy changes, failed access attempts, and mass deletion events.
If you are using S3-compatible storage, such as a MinIO-based object storage service, these principles still apply. Compatibility makes it easier to use familiar backup tools, developer libraries, and application workflows. It does not eliminate the need to configure permissions, keys, and retention policies correctly.
Make security part of your launch process
The fastest teams do not wait for an audit or a breach to organize access. They create a repeatable launch checklist for every new bucket, website, client project, or application environment. Decide whether the data is public or private, create scoped credentials, set encryption and retention rules, and record who owns the bucket.
Centralized infrastructure can make this easier because your domains, websites, backups, cloud workloads, and storage can be managed with clearer ownership instead of spread across disconnected accounts. ACMMAX customers can use that operational visibility to keep storage aligned with the systems it supports.
Object storage should help your business move faster, not create a hidden risk behind every upload. Set the rules early, test recovery when nothing is urgent, and give your team a storage setup they can use confidently as the business grows.